One fraudulent email, one careless employee, or one overlooked warning can expose sensitive borrower information and put an agency’s reputation and client relationships at risk.
Many asset recovery agencies still treat cybersecurity as something only the IT department handles, if they even have an IT department, which most smaller agencies cannot afford. That thought process is convenient but dead wrong. Today’s lending clients entrust your agency with consumer information the government refers to as “Non-Public Personal Information” (NPPI) and how you protect that information has become a major concern.
It is your responsibility to protect the NPPI entrusted to your recovery agency and you should recognize that many of today’s attacks don’t begin by breaking code. Instead, they begin by persuading one of your employees to act on an urgent email that appears to come from a legitimate source, to trust a person posing as a help desk, or even, as I recently witnessed at a member agency, to pay a vendor invoice that arrived with new banking details.
Whether you recognize it or not, as agency leaders we must realize that the weakest point in our systems is often human behavior, every leader who directs people or controls finance plays a critical security role and should be aware of scams, phishing attacks, malware, and the numerous illegal schemes devised by cyber criminals and hackers to steal protected data.
In today’s asset recovery agencies, cybersecurity is a test of stewardship. Our clients and their customers trust us with their livelihoods, their borrower’s personal information, and their business reputation. Protecting that trust cannot be handed off entirely to the IT specialists, any more than integrity can be relegated to the legal department.
Recovery agency owners, managers and unit leaders who model good habits, build sound systems, and prepare their subordinates to stay vigilant against the threat of a cyber breach do more than manage the risk. They show they take seriously all the personal and protected data placed in their care.
Cyber defense and data protection begins with recognizing and instituting the right behavior.
Agency employees pay closer attention to what the agency leaders do than to what policy says. A leader who shares passwords, skips multi-factor authentication, or asks an assistant to send a sensitive file to a personal email account teaches everyone that convenience outweighs protection.
The opposite is just as powerful. Agency leaders who verify unusual requests, follow the same rules they ask of others, and double-check the details before releasing protected information make caution and diligence the mark of good judgment.
Even more importantly, the agency leaders must develop a “Safe Harbor” for employees to report mistakes or breaches quickly. The employee who clicks a bad link and says so within minutes is an asset, not a problem. The one who hides it for fear of blame can turn an incident into a serious data breach.
Cybersecurity is now, and always has been, a set of choices about risk, and those choices are at the agency’s leadership table, not solely with IT. What data the recovery agency collects and stores, how long the data is kept, who can access what, which outsiders and vendors are trusted, and which controls are worth their costs are decisions the agency leaders make.
Knowledgeable leaders build programs that withstand the influence of any one person. They require two approvals for large payments, confirm any change in account details through a second channel, and ensure access ends when a role ends.
Knowledgeable leaders educate their employees of various scams, phishing schemes, and cyber intrusion tactics used to steal data and follow up the initial training with continuing education.
None of this requires a leader to become an information technologist. It requires the same judgment leaders already apply to people, projects, and metrics. Attackers count on busy people who trust too quickly and leaders who assume someone else is watching.
The recovery agency leaders who earn lasting trust are those who take the job of cybersecurity seriously and stay vigilant against the threat. Data security is now a major issue for all agency leaders, in all areas of operations, and at all times.
Don’t miss the CYBER SECURITY ARC 10 session at the AFA Mid-Year Conference next week in San Antonio Texas.
Recovery Agencies Are One Click Away from a Cybersecurity Disaster – Recovery Agencies Are One Click Away from a Cybersecurity Disaster – Recovery Agencies Are One Click Away from a Cybersecurity Disaster
Ron L. Brown MCE, IFCCE, MPRS, CCCO, CARS, CFA
CSI GROUP / EAGLE GROUP XX / NAFI / API0217
The Eagle Group XX/USA Creed is,
“Anything, Anytime, Anyplace… Professionally”
Talk Is Cheap, Repossession Isn’t. Get Off Your Knees: The Eagles Draw a Line on Repo Fees – Talk Is Cheap, Repossession Isn’t. Get Off Your Knees: The Eagles Draw a Line on Repo Fees – Talk Is Cheap, Repossession Isn’t. Get Off Your Knees: The Eagles Draw a Line on Repo Fees
For more information on Eagle Group XX/USA visit www.eaglegroupxx.com or contact Ron Brown at 800-411-1844 or Rbrown@CSI-ARM.com
Related:
In The Future Will There Be Anyone Left to Recover Vehicles?
Talk Is Cheap, Repossession Isn’t. Get Off Your Knees: The Eagles Draw a Line on Repo Fees
Recovery Agencies Are One Click Away from a Cybersecurity Disaster – Eagle Group XX – Eagle Group XX – Training – Compliance – Data – Data – Repossess – Repossession – Repossession Agency – Repossessor – Repossession – Repossession News – Fraud – Fraud

More Stories
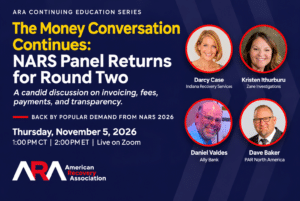
The Money Conversation Continues: NARS Panel Returns for Round Two
Conflicting Repo Rulings Prompt ARA Call for Industry Reform
New On Hook Episode: A Conversation with Bahador Rahimi
Meet Otto: Your New AI Assistant in Clarity
NARS 2027 Industry Award Nominations Are Open
Beyond the Camera: A New Standard for Agent Safety and Field Protection